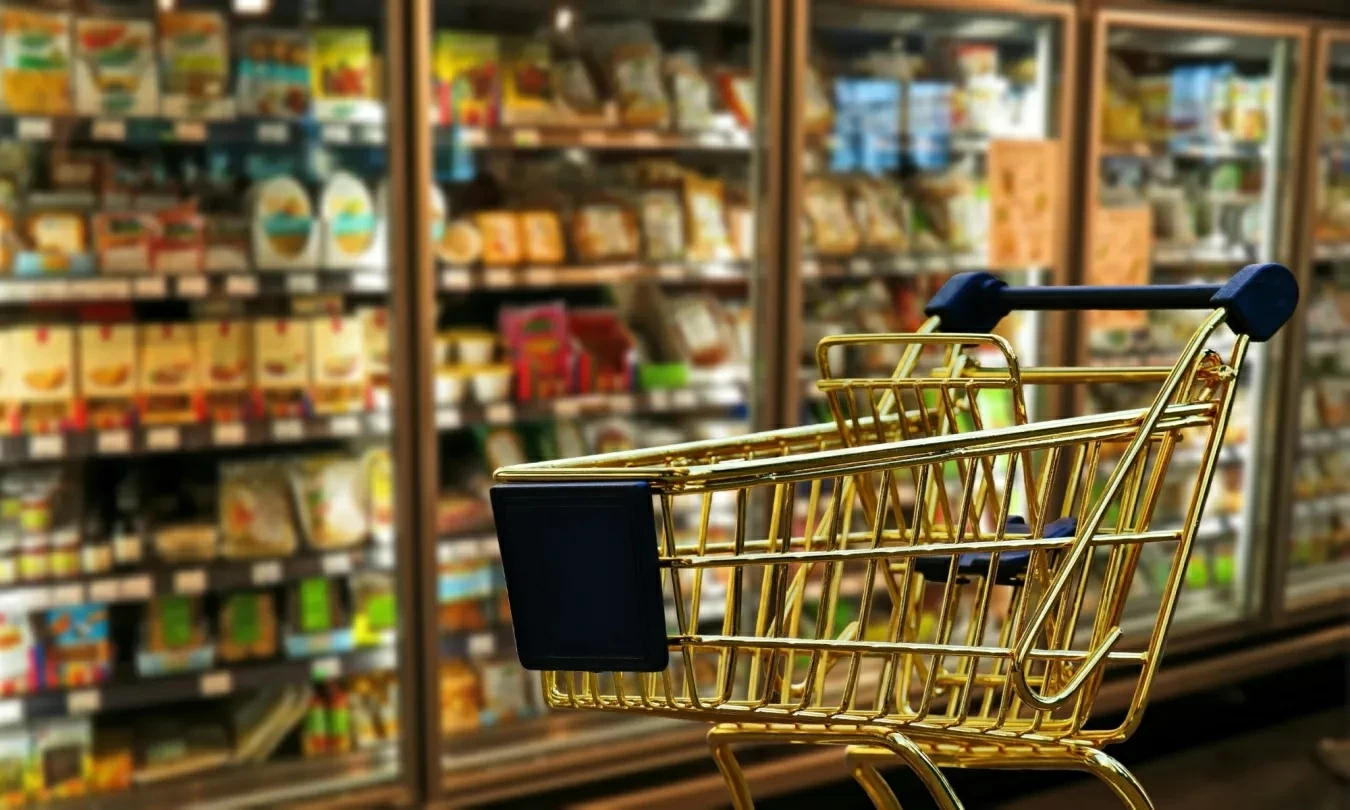
لم تعد الهجمات الإلكترونية تستهدف البيانات والأموال فحسب، بل امتدت إلى ما هو أبعد من ذلك، لتصل إلى ثلاجات حفظ الأغذية داخل المتاجر الكبرى، في تطور خطير كشف عن قدرة القراصنة على إحداث خسائر مادية مباشرة دون الحاجة إلى سرقة أي معلومات. فقد شهدت عدة دول أوروبية هجمات استهدفت أنظمة التبريد والتحكم في درجات الحرارة، بعدما تمكن مهاجمون من التلاعب بإعداداتها عن بُعد، وتحويل وحدات التبريد إلى أجهزة تسخين تسببت في إفساد كميات من المنتجات الغذائية.
وشملت الهجمات متاجر في بلجيكا والسويد ولوكسمبورغ وإيرلندا وإستونيا، وسط مخاوف من اتساع نطاق هذه العمليات، خصوصاً أنها استهدفت أنظمة تشغيلية تتحكم بشكل مباشر في ظروف تخزين الأغذية، بدلاً من التركيز على اختراق أجهزة الحاسوب أو الاستيلاء على البيانات.
وبحسب تقارير تقنية، استغل المهاجمون ثغرات في أنظمة التحكم الرقمية الخاصة بوحدات التبريد، وتمكنوا من تغيير إعداداتها عن بُعد، ما أدى إلى ارتفاع درجات الحرارة داخل الثلاجات والمجمدات إلى مستويات غير طبيعية.
وفي بلجيكا، تعرضت متاجر تابعة لسلسلة «Delhaize» لاستهداف أنظمة التبريد، إذ أوضح مسؤول في شركة متخصصة بهذا المجال أن القراصنة تمكنوا من تحويل وحدات التبخير إلى وضع إزالة الجليد (Defrost Mode).
وتُستخدم هذه الخاصية عادة للتخلص من الجليد المتراكم داخل وحدات التبريد، إلا أن تفعيلها في هذه الحوادث أدى إلى ارتفاع درجات الحرارة بدلاً من الحفاظ على برودة المنتجات، ما تسبب في تلف كميات من الأغذية.
وسجلت بعض الحوادث ارتفاع درجة الحرارة داخل مجمدات أحد متاجر سلسلة «ICA» السويدية إلى نحو 50 درجة مئوية، فيما وصلت الحرارة داخل ثلاجات إحدى شركات الجزارة في بلجيكا إلى 18 درجة مئوية، متسببة في إفساد لحوم تُقدر قيمتها بنحو 15 ألف يورو.
هجمات تطال سلاسل تجارية كبرى
لم تقتصر الهجمات على متاجر محدودة، بل امتدت إلى عدد من العلامات التجارية المعروفة في أوروبا، ما يعكس اتساع نطاق الاستهداف وتعدد الجهات المتضررة.
وفي بلجيكا، تأثر 15 متجراً تابعاً لسلسلة «Carrefour»، إلى جانب متاجر «Delhaize»، كما شملت الهجمات خمسة متاجر تابعة لمجموعة «Colruyt».
أما في السويد، فقد طالت سبعة متاجر تابعة لسلسلة «Coop»، إضافة إلى عدد محدود من متاجر «ICA»، بينما أعلنت سلسلة «SuperValu» في إيرلندا تأثر 13 متجراً بالهجمات.
وامتد الاستهداف أيضاً إلى أحد متاجر «IKEA» في بلجيكا، فيما شهدت إستونيا هجوماً تمكنت الفرق الفنية من احتوائه خلال دقائق، دون تسجيل أضرار كبيرة.
فرنسا شهدت هجمات مماثلة
وتأتي هذه الحوادث بعد موجة هجمات إلكترونية مماثلة شهدتها فرنسا خلال أكتوبر الماضي، واستهدفت مئات المتاجر الكبرى والمحال المستقلة، بعدما تمكن المهاجمون من التلاعب بأنظمة التبريد ورفع درجات الحرارة داخل بعض الوحدات إلى نحو 50 درجة مئوية.
ولفتت التقارير إلى أن بعض الأنظمة المتضررة في الهجمات الأوروبية تعتمد على تقنيات للتحكم في درجات الحرارة من شركة «Danfoss» الدنماركية، وهي الشركة التي ظهرت تقنياتها أيضاً ضمن الأنظمة المستهدفة في فرنسا.
من جانبها، أكدت الشركة أنها تعمل مع عملائها لمعالجة المشكلات الأمنية واتخاذ التدابير اللازمة للحد من المخاطر المرتبطة بهذه الحوادث.
تحقيقات أوروبية لكشف المتورطين
وأعادت الهجمات تسليط الضوء على المخاطر الأمنية التي تواجه الأنظمة الصناعية والتجارية المتصلة بالإنترنت، بعدما أثبتت أن اختراق هذه الأنظمة قد يتجاوز تعطيل الخدمات أو تسريب المعلومات، ليصل إلى إتلاف المنتجات والتسبب في خسائر مالية مباشرة.
وأعلن مركز الأمن السيبراني البلجيكي علمه بالهجمات، فيما باشرت النيابة العامة الفيدرالية تحقيقاً للكشف عن ملابساتها والجهات المسؤولة عنها.
وحتى الآن، لم تعلن أي جهة مسؤوليتها عن هذه العمليات، كما لم يتأكد وجود ارتباط مباشر بين الهجمات الأخيرة وتلك التي استهدفت متاجر في فرنسا خلال الشهر الماضي.
وفي سياق متصل، حذر مفوض الاتحاد الأوروبي للزراعة، كريستوف هانسن، من أن تكرار مثل هذه الحوادث يمثل تهديداً لسلاسل إمدادات الغذاء، فضلاً عن تأثيره المحتمل على ثقة المستهلكين في سلامة المنتجات الغذائية.
Cyberattacks are no longer just targeting data and money; they have extended beyond that to reach food storage refrigerators inside major stores. This serious development has revealed the hackers' ability to cause direct material losses without the need to steal any information. Several European countries have witnessed attacks targeting cooling and temperature control systems after attackers managed to manipulate their settings remotely, turning refrigeration units into heating devices that spoiled large quantities of food products.
The attacks included stores in Belgium, Sweden, Luxembourg, Ireland, and Estonia, amid fears of the expansion of these operations, especially since they targeted operational systems that directly control food storage conditions, rather than focusing on hacking computers or seizing data.
According to technical reports, the attackers exploited vulnerabilities in the digital control systems of refrigeration units, managing to change their settings remotely, which led to abnormal temperature increases inside refrigerators and freezers.
In Belgium, stores belonging to the "Delhaize" chain were targeted, with a company official in this field explaining that the hackers managed to switch the refrigeration units to defrost mode.
This feature is usually used to remove accumulated ice inside refrigeration units; however, activating it in these incidents led to temperature increases instead of maintaining the coolness of the products, resulting in the spoilage of quantities of food.
Some incidents recorded temperature rises inside the freezers of one of the "ICA" chain stores in Sweden to about 50 degrees Celsius, while the temperature inside the refrigerators of a butcher shop in Belgium reached 18 degrees Celsius, causing the spoilage of meat valued at around 15,000 euros.
Attacks on Major Retail Chains
The attacks were not limited to a few stores but extended to several well-known brands in Europe, reflecting the widening scope of targeting and the diversity of affected parties.
In Belgium, 15 stores belonging to the "Carrefour" chain were affected, along with "Delhaize" stores, and the attacks also included five stores belonging to the "Colruyt" group.
In Sweden, seven stores belonging to the "Coop" chain were targeted, in addition to a limited number of "ICA" stores, while the "SuperValu" chain in Ireland announced that 13 stores were affected by the attacks.
The targeting also extended to one of the "IKEA" stores in Belgium, while Estonia experienced an attack that technical teams managed to contain within minutes, without significant damage being recorded.
France Experienced Similar Attacks
These incidents come after a wave of similar cyberattacks that occurred in France last October, targeting hundreds of major stores and independent shops, after attackers managed to manipulate cooling systems and raise temperatures inside some units to about 50 degrees Celsius.
Reports indicated that some of the affected systems in the European attacks rely on temperature control technologies from the Danish company "Danfoss," which also had its technologies featured among the targeted systems in France.
For its part, the company confirmed that it is working with its clients to address security issues and take necessary measures to mitigate the risks associated with these incidents.
European Investigations to Uncover the Perpetrators
The attacks have once again highlighted the security risks facing industrial and commercial systems connected to the internet, after proving that breaching these systems can go beyond disrupting services or leaking information to include damaging products and causing direct financial losses.
The Belgian Cybersecurity Center announced its awareness of the attacks, while the federal public prosecutor's office has initiated an investigation to uncover the circumstances and responsible parties.
So far, no party has claimed responsibility for these operations, nor has there been any confirmed direct link between the recent attacks and those that targeted stores in France last month.
In a related context, the European Commissioner for Agriculture, Christoph Hansen, warned that the recurrence of such incidents poses a threat to food supply chains, as well as its potential impact on consumer confidence in the safety of food products.